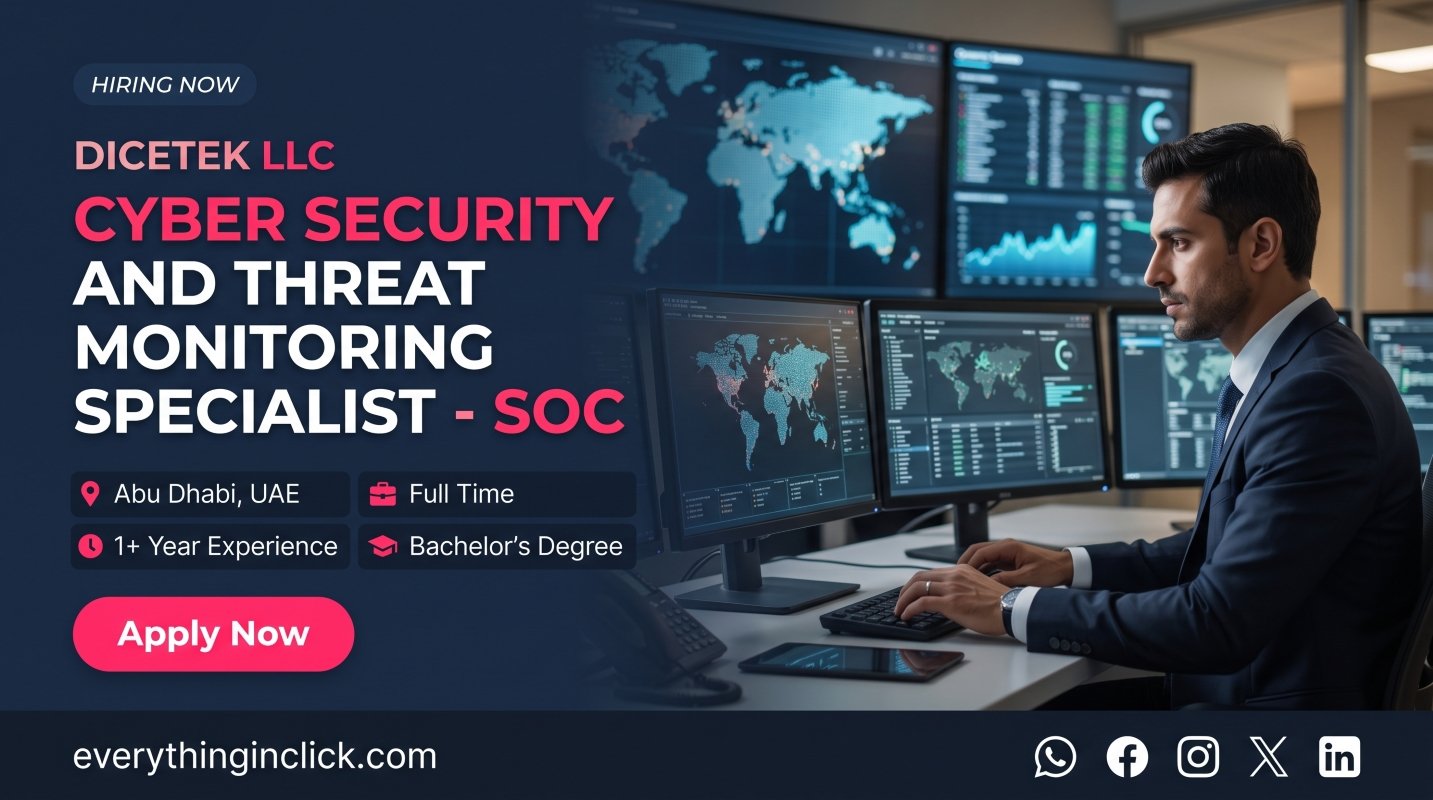
Cyber Security and Threat Monitoring Specialist – SOC
Job Details
Job Title:
Cyber Security and Threat Monitoring Specialist - SOC
Department:
Cyber Security
Location:
Abu Dhabi, UAE
Job Type:
Full Time
Salary:
TBD
Job Description of Cyber Security and Threat Monitoring Specialist - SOC
✅ Dicetek is looking for a Cyber Security and Threat Monitoring Specialist to join its Security Operations Center (SOC) in Abu Dhabi. You will be on the front line of defence, watching over cloud, endpoint and network environments around the clock, spotting threats early and responding fast. This is a hands-on role for someone who likes investigation work, enjoys automation and wants to build a career in security operations on enterprise-scale projects.
Key Responsibilities of Cyber Security and Threat Monitoring Specialist - SOC
✅ Monitor security events and alerts in a 24x7 SOC environment.
✅ Investigate and triage incidents using SIEM platforms such as Microsoft Sentinel, Splunk or QRadar.
✅ Lead and support incident response, from detection and containment through to recovery and reporting.
✅ Proactively hunt for threats across cloud, endpoint and network environments.
✅ Build and tune detection rules and use cases to improve coverage and cut false positives.
✅ Develop SOAR playbooks and automations to speed up response.
✅ Run security operations in line with NIST and ISO 27001 frameworks.
✅ Document incidents, escalate them appropriately and contribute to continuous improvement of SOC processes.
Qualification Required for Cyber Security and Threat Monitoring Specialist - SOC
✅ Bachelor’s degree in a relevant field.
✅ 1+ year of experience in security operations or a related role.
✅ Experience with 24x7 SOC operations (shift work).
✅ SIEM investigation using Microsoft Sentinel, Splunk, QRadar or equivalent.
✅ Incident response and threat hunting.
✅ Cloud, endpoint and network security monitoring.
✅ SOAR automation and detection engineering.
✅ Working knowledge of NIST and ISO 27001-aligned security operations.
✅ SC-200, AZ-500, CEH, Security+, CySA+ or equivalent.